
A hidden remote-access agent was planted on online poker players' Windows PCs through two compromised poker tools, according to a report published on September 29, 2026 by cybersecurity researcher @wolfsec0x0. Whoever controlled it could watch those screens live, hole cards included.
The researcher estimates between 10 and 30 players in Europe, North America and Oceania were hit, mostly high-stakes regulars. The earliest confirmed activity is from March 16, 2024, and on some PCs the agent stayed for more than a year, according to the researcher's full public report.
A PC that looks clean still needs checking. On September 27 the operator was seen uninstalling the agent remotely and deleting the scripts used to do it, but registry keys survive that clean-up, and some PCs still carry a Defender exclusion covering the whole Windows folder.
The researcher is not naming the two tools. One of them, table manager IntuitiveTables, has told users it was targeted, and separate allegations name the accounts said to be behind the attack. No poker site's own software is known to be involved.
| Detail | What We Know |
|---|---|
| Report published | September 29, 2026, by @wolfsec0x0 |
| Players affected | 10 to 30 (researcher's estimate) |
| Where | Europe, North America, Oceania |
| Who was targeted | Mainly high-stakes regulars |
| First confirmed activity | March 16, 2024 |
| How it spread | Two compromised, code-signed poker tools |
| Tools named | IntuitiveTables (its own statement); second tool unconfirmed |
| Poker site software | Not known to be involved |
| What the attacker could see | The live screen, including hole cards |
| Status | Removed or disabled on every confirmed PC |
What the Poker Malware Report Confirms
The agent belongs to MeshCentral, legitimate open-source software that companies use to manage computers remotely. On the affected PCs it was installed without the owner's knowledge, ran as a Windows service with full system privileges and connected to a server run by a third party.
⚠️ Online poker players: we've confirmed a covert remote-access agent planted on players' Windows PCs through compromised poker software.
Current estimate: ~30 users affected, in several countries across Europe, North America and Oceania.
Details and checks below 🧵
— WolfSec0x0 (@wolfsec0x0) September 29, 2026
According to the report, it contains only findings backed by preserved evidence, analysis of the software itself or a vendor's own confirmation. Affected players, vendors and products are all left unnamed.
What the Attacker Could Do
For as long as the agent was connected, whoever ran the server had the same access as someone sitting at the keyboard. The report lists four capabilities:
- Watch the screen live: including a player's own hole cards during real-money play.
- Take over the mouse and keyboard: the PC could be operated remotely.
- Run commands with SYSTEM privileges: the highest level of access on Windows.
- Copy files to and from the PC: anything stored on the machine was reachable.
That reach went well beyond the poker table. Browser-saved passwords, saved payment cards and session cookies were all exposed, and the report warns that stolen session cookies can get past passwords and two-factor authentication until those sessions are revoked.
How It Reached Players' PCs
Both delivery routes ran through legitimate Windows utilities that poker players install themselves, each signed with its vendor's code-signing certificate. The report calls them Tool A and Tool B:
- Tool A: the vendor has confirmed the compromise. On September 29 it matched install dates from July and August 2025 to a compromised version of its software.
- Tool B: the researcher found a backdoored build by analysing its code. It was signed with the vendor's valid certificate in early March 2026, one day after a clean build, and the vendor has not yet confirmed it.
Why the signature did not help: Windows and antivirus software treat a validly signed program as trustworthy. A backdoored build signed with the vendor's own certificate looks exactly like a genuine update, which is why the report tells vendors to verify every update package before it runs.
Mesh Agent Timeline: March 2024 to the Report
The report's timeline runs from the first remote session to the vendor's confirmation. Every date below comes from evidence on affected PCs or from a vendor.
| Date | Event |
|---|---|
| March 16, 2024 | Earliest confirmed activity: remote command-line sessions on an affected PC |
| April 2024 | Agent activity on a further PC |
| October 2024 | Agent installed on a further PC |
| June to August 2025 | More PCs infected; Vendor A later tied the July and August installs to Tool A |
| October 2025 to June 2026 | Agent reinstalled repeatedly on one PC |
| Early March 2026 | Backdoored Tool B build signed with the vendor's valid certificate |
| September 26 to 28, 2026 | Affected players begin disabling the agent |
| September 27, 2026 | Operator seen uninstalling the agent remotely with self-deleting scripts |
| September 29, 2026 | Vendor A confirms; report published |
Why the clean-up matters: the operator removed the agent from some PCs before the report went public. Task Manager will show nothing on those machines, which is why the checks below look for the traces the agent leaves behind.
How to Check Your PC for Mesh Agent
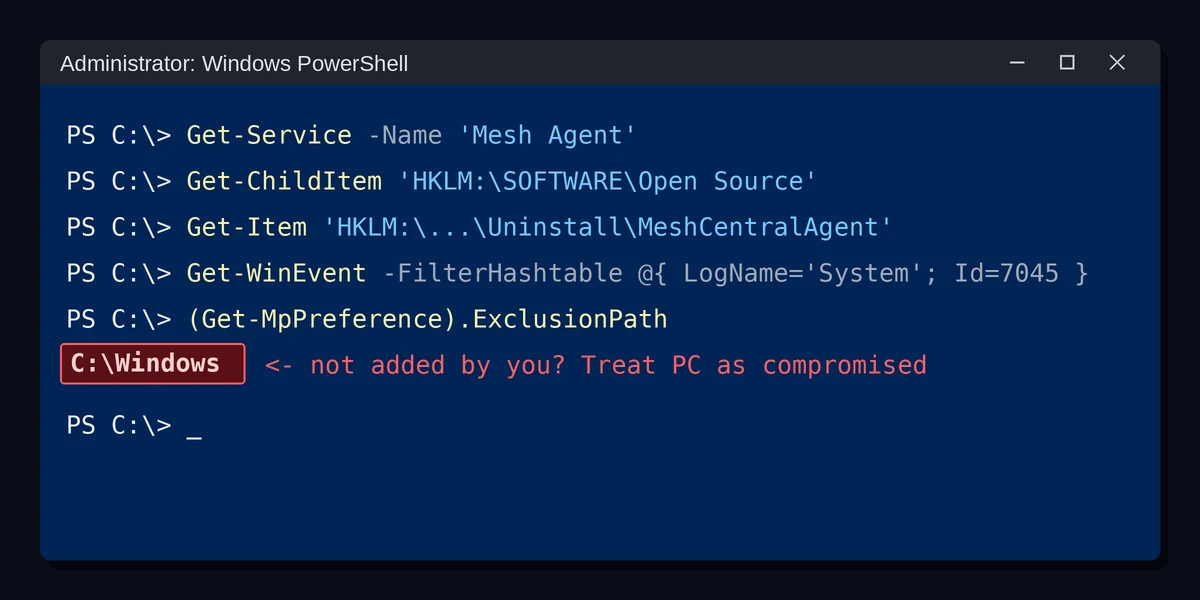
The report publishes five read-only checks. None of them changes anything on your PC. Open PowerShell as administrator, because Windows only shows Defender exclusions to administrators, and run:
Get-Service -Name 'Mesh Agent' -ErrorAction SilentlyContinue
Get-ChildItem 'HKLM:\SOFTWARE\Open Source' -ErrorAction SilentlyContinue
Get-Item 'HKLM:\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\MeshCentralAgent' -ErrorAction SilentlyContinue
Get-WinEvent -FilterHashtable @{ LogName = 'System'; Id = 7045 } -ErrorAction SilentlyContinue | Where-Object { $_.Message -match 'Mesh Agent' } | Select-Object TimeCreated, Message
(Get-MpPreference).ExclusionPath
Here is what each line looks for and what a result means:
| Check | What It Finds | If It Returns Anything |
|---|---|---|
| Mesh Agent service | The agent running as a service | The agent is installed now |
| Open Source registry key | Keys left behind after removal | The agent is or was present |
| MeshCentralAgent uninstall key | The agent's uninstall entry | The agent is or was present |
| System event 7045 | When the service was created | Shows the install date |
| Defender exclusions | Folders Defender does not scan | C:\Windows listed: treat the PC as compromised |
The Defender Check Most Players Skip
The first four commands find the agent or its leftovers. The fifth catches something else: on affected PCs, Microsoft Defender had been told to ignore the entire C:\Windows folder.
On one PC that exclusion was removed two minutes after it was added. On others it is still in place, so Defender scans nothing in that folder. If C:\Windows is listed and you did not add it, treat the PC as compromised even if no agent turns up.
When MeshCentral Is on Your PC for a Reason
MeshCentral is used by employers and IT providers to manage computers, so a work laptop may carry it legitimately.
Rule of thumb: if nobody you trust set up MeshCentral on the machine, assume the agent is hostile and follow the steps below.
What to Do If You Find Mesh Agent on Your PC
The report's steps run in this order for a reason: preserve the evidence first, then lock down your accounts from a machine the attacker cannot see.
- Disconnect the PC from the internet: do not delete anything yet, because police and poker sites will want the evidence.
- Switch to a different, clean device: change your email password first, then your poker site, crypto exchange and other passwords.
- Sign out everywhere: end every active session and turn on two-factor authentication wherever you can.
- Replace saved cards: ask your card issuer to replace any card saved in a browser on that PC.
- Empty software wallets: move funds out of any software crypto wallet installed on it.
- Report it: tell the security team of every poker site you play on, and your local police or fraud-reporting service.
- Wipe and reinstall Windows: once the evidence is collected, because removing the agent alone is not enough.
British online pro Patrick Leonard called the attack one of the biggest things to happen in online poker. He urged anyone who has played on desktop in recent years, especially higher-stakes cash players using third-party tools, to follow the thread and change their passwords.
This is one of the biggest things that has happened in online poker, how we react to it as a community and individuals is very important. If you’ve played online on a desktop in the last few years (and especially if higher stakes cash and used any 3rd party tools) please follow… https://t.co/z1PQ1y83vN
— Patrick Leonard 🫡 (@padspoker) September 29, 2026
Which Poker Tools Were Compromised?
The report withholds the names of both tools and their vendors, and the researcher's thread says the products are not being named publicly. The only name confirmed so far has come from a vendor itself.
IntuitiveTables Says It Was Targeted
Table manager IntuitiveTables issued a statement to its users, read out by Charlie Carrel in a YouTube video on September 30. The key points:
- Targeted: a known cheater went after several applications to install spyware on the devices of specific high-stakes players, and IntuitiveTables was one of them.
- Scale: the company put the number of affected players at around 30 worldwide.
- Investigation: it has opened a full-scale investigation into what happened.
- Current versions: its team verified that the versions currently available to the public contain no malicious code.
The statement as read out did not say which versions were affected or when they were served. Whether IntuitiveTables is the report's Tool A or Tool B is not public.
The Second Tool Is Still Unconfirmed
The other vendor has not confirmed that its build was tampered with, and no other tool has been named with evidence behind it. Until it is, anyone who runs third-party poker utilities on a high-stakes machine should run the checks above.
Who Is Accused of Being Behind It?
The researcher's report names no one and does not link the agent to any poker account. The accusations come from elsewhere.
Tournament regular Alexey “Avr0ra” Borovkov alleged on his Telegram channel that the operator played on GGPoker as Paul Gregg and on the Winning Poker Network under the names OxOO, JackKlompus and Ez[Pz]. Carrel repeated the Paul Gregg name in his video.
The researcher has also stressed that the poker sites' own clients are not the problem. In a follow-up post on X, wolfsec0x0 said no poker client is known to be malicious or infected, and that GGPoker, WPN, CoinPoker and WPT Global are not involved.
What the WPN Account Data Shows
On September 30, Run It Once coach Frankie Carson, who plays mid and high-stakes online cash games, posted results-tracking data for the two WPN accounts named in the allegations. The figures come from a third-party tracking site, not from WPN.
| Account | Period, per Carson | Hands | Winnings | Win Rate (bb/100) |
|---|---|---|---|---|
| JackKlompus | Early 2024 to summer 2025 | 32.2k | $402.7k | 24.3 |
| OxOO | October 2025 onwards | 37.4k | $423.5k | 11.4 |
Carson alleges the operator played as JackKlompus until the summer of 2025, stepped away as players began to work him out, and returned in October as OxOO. He also claims OxOO lost on purpose at low and mid stakes to drag its overall win rate down.
Paul Gregg started in early 2024 on WPN as JackKlompus making $400k winning at +24bb/100 vs the best in the world.
He started feeling the pressure of people figuring him out, so in the summer of last year he stopped playing before resuming in October under the new screenname OxO… pic.twitter.com/9vguHebGAA
— Frankie Carson (@FrankieCPoker) September 30, 2026
The OxOO data shows small losses at most stakes from NL10 to NL1000. Its biggest win came at NL10000: $195.3k over 5.5k hands at 35.5bb/100, or 35.5 big blinds won per 100 hands.
What the data does and does not show: these are winnings recorded by a tracking site, not results confirmed by WPN, and they show that the accounts won rather than how. No WPN statement on either account has been published.
How the Mesh Agent Case Compares to Past Superuser Scandals
Online poker has seen hole cards exposed before. The closest precedent is a Danish case from more than a decade ago.
| Case | Period | Method | Hole Cards Seen? | Outcome |
|---|---|---|---|---|
| UltimateBet and Absolute Poker | Exposed 2007 to 2008 | Insider superuser accounts | Yes | $22.1M refunded, no charges |
| Peter Jepsen | 2008 to 2014 | Spyware on opponents' computers | Yes | 3 years in prison |
| MoneyTaker69 on GGPoker | 2023 | Modified game client | No, all-in equity only | Banned, $29,795 refunded |
| Mesh Agent | 2024 to 2026 | Compromised third-party tools | Yes, via the live screen | Under investigation |
Danish pro Peter Jepsen installed spyware on opponents' computers so he could see their screens, and their cards, when he played them online. In December 2020 the Danish appeal court's ruling gave him three years for hacking and fraud.
The court also confiscated DKK 22.4 million. Jepsen is one of only four players in our list of every poker pro sentenced to prison who were jailed for cheating at the game itself.
The 2023 GGPoker case looked like a hole-card breach at first but was something narrower. The MoneyTaker69 client exploit on GGPoker let one player deduce all-in equity, and GGPoker patched the client and banned the account.
Russ Hamilton was never charged over the UltimateBet superuser accounts, a pattern that runs through poker's long record of cheating scandals.
What Happens Next
This story is still developing. These are the things to watch:
- The second vendor: whether Tool B's maker confirms the backdoored build, and whether either vendor names the affected versions.
- IntuitiveTables' investigation: which versions were served, when, and to how many users.
- The poker sites: the report asks them to review table histories for accounts that sat with affected players unusually often. Any bans or refunds would follow from that.
- Law enforcement: the report tells affected players to go to the police. No police investigation has been announced.
- More infected PCs: the estimate of 10 to 30 includes cases not yet confirmed, and the operator removed the agent from some machines.
- The accused accounts: no response from the people behind the accounts named by Borovkov has been published.
We will update this article as the vendors, the sites and the researcher publish more. The next developments will appear in our online poker news coverage.
FAQs
What is Mesh Agent?
Mesh Agent is the Windows service installed by MeshCentral, legitimate open-source remote-management software. In this case it was planted on poker players' PCs without their knowledge through two compromised poker tools, letting the attacker watch their screens, hole cards included, and control the machines.
How do I check if my PC has Mesh Agent?
Open PowerShell as administrator and run Get-Service ‘Mesh Agent' and Get-ChildItem ‘HKLM:\SOFTWARE\Open Source'. Then run (Get-MpPreference).ExclusionPath. If C:\Windows appears and you did not add it, treat the PC as compromised even if no agent shows up.
Which poker tools were compromised?
The researcher is not naming the two tools. IntuitiveTables has told users it was one of the applications targeted and says its current public versions are clean. The second tool's vendor has not confirmed a compromise.
Were GGPoker or ACR Poker hacked?
No poker site's own software is known to be involved. The researcher said the GGPoker, WPN (home of ACR Poker), CoinPoker and WPT Global clients are not involved. The agent reached players' PCs through third-party tools, not through the poker clients.
How many players were affected?
The researcher estimates between 10 and 30 players in Europe, North America and Oceania, mostly high-stakes regulars. The agent has been confirmed on multiple PCs, and the estimate includes suspected cases that are not yet confirmed.
Who is accused of being behind the attack?
Alexey Borovkov alleged on Telegram that the operator played as Paul Gregg on GGPoker and as OxOO, JackKlompus and Ez[Pz] on WPN. Tracking data posted by coach Frankie Carson shows each WPN account winning more than $400,000. Nobody has been charged, no site has confirmed a link, and the researcher's report names no one.
